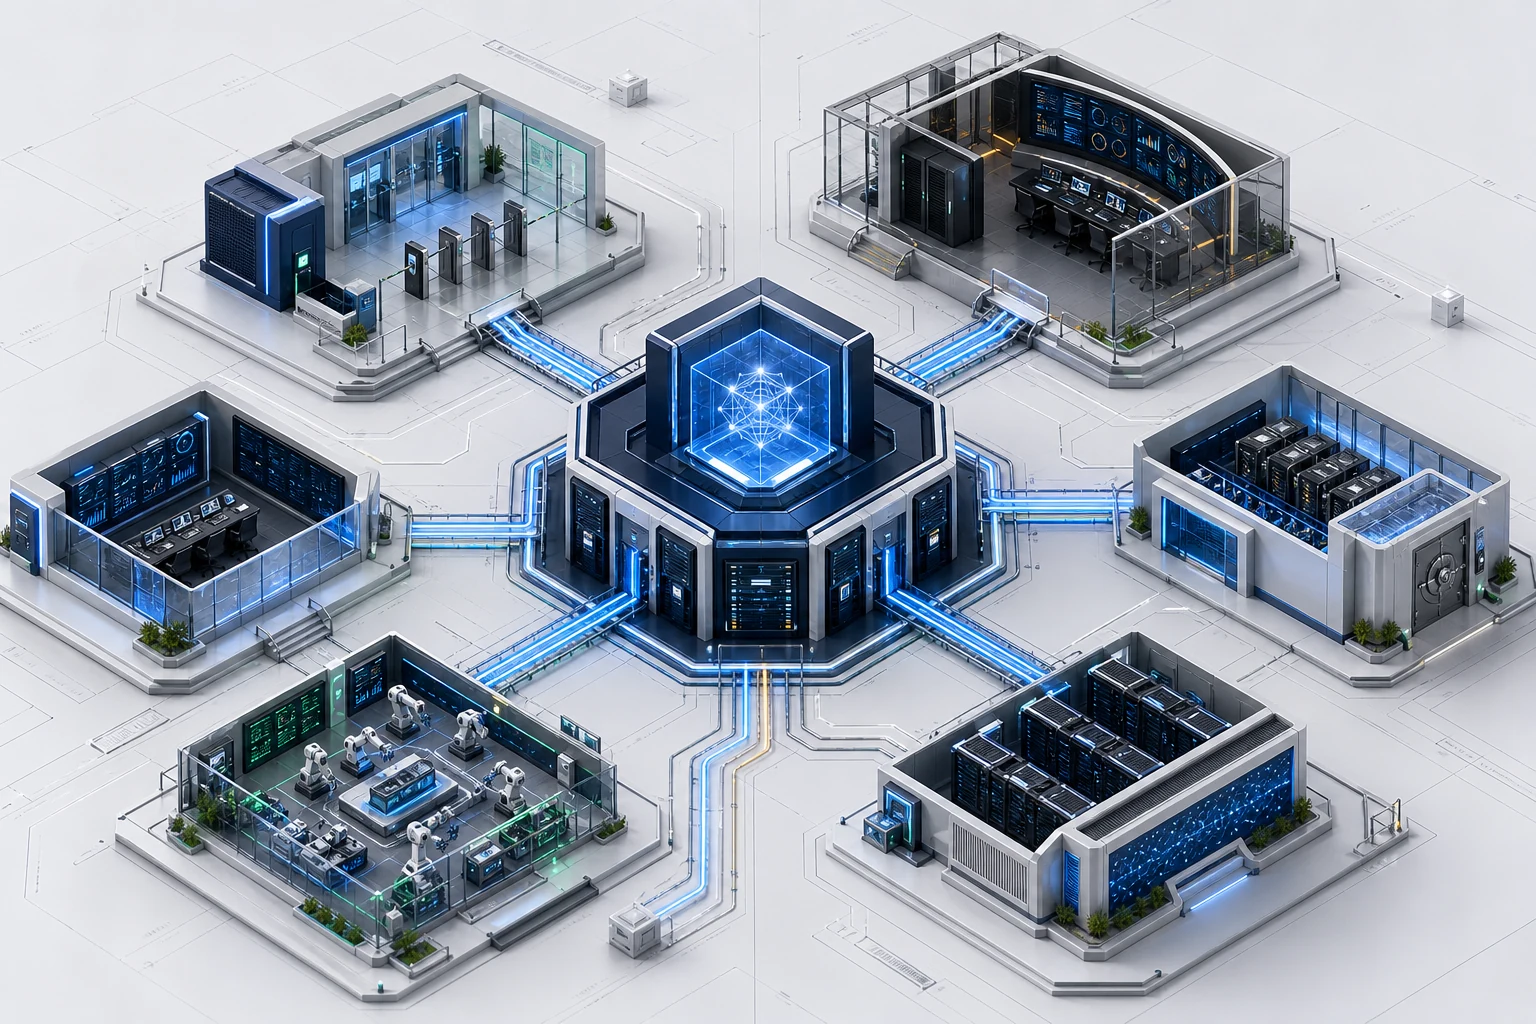
Fragmented knowledge
Important information is distributed across documents, systems, departments and previous assessments.
PRIVATE AI FOR GOVERNANCE, RISK AND COMPLIANCE
Governed intelligence. Built for critical work.
AKRITES transforms approved organizational knowledge into structured GRC deliverables, supervised agent workflows and verifiable evidence inside your controlled environment.
Private deployment options · Approved knowledge sources · Human-in-the-loop controls · Source-based outputs · Auditable activity and evidence
AKRITES combines private infrastructure, approved knowledge, defined controls, human authority and evidence by design.
The business problem
Compliance teams regularly search through policies, standards, risk registers, previous assessments, technical documentation and evidence repositories. They then repeat the same work across audit plans, reports, reviews, questionnaires and remediation activities.
Generic AI tools may reduce drafting time, but they also introduce concerns about sensitive data, unsupported answers, inconsistent outputs and unclear accountability.
AKRITES combines private AI, approved enterprise knowledge, structured playbooks, human approval gates and audit evidence in one controlled platform.
Important information is distributed across documents, systems, departments and previous assessments.
Experts repeatedly collect evidence, compare requirements, structure reports and chase process owners.
Reports and assessments may differ depending on the author, available time and source material.
Public AI services can create concerns around confidential information, traceability and governance.
Product demonstration
A realistic AKRITES workspace connects scope, approved sources, generated outputs and human review in one controlled workflow.
Product demonstration
AI accelerates the work. Accountable professionals remain in control.
Choose an approved GRC task, template or playbook.
Define organization, scope, framework, systems, processes and objectives.
AKRITES searches only the knowledge sources that the user or role is authorized to access.
The platform produces a structured draft, identifies missing information and links relevant statements to supporting sources.
Responsible professionals review, edit, approve, reject or request additional information.
Sources, versions, approvals, actions and workflow events are recorded for traceability.
GRC solutions
AKRITES supports focused, repeatable workflows across audit, risk, privacy, security and business continuity.
Controlled automation
Human control does not disappear as automation increases. Ownership, approval authority, escalation and the ability to stop a workflow become more explicit.
Search, summarize, compare and draft using approved internal knowledge. The assistant supports employees but does not execute business actions.
People make business decisions and execute process actions.
Source-based answers
Agents follow approved multi-step playbooks, use permitted tools and pause at defined human approval gates.
Agents wait for the required human approval before controlled actions continue.
Workflow events and approvals
Agents execute mature workflows within a fixed scope, defined policies, tool limits, exception rules and escalation paths.
Execution remains within the approved scope, permissions and stop conditions.
Action logs, exceptions and evidence records
Why AKRITES
Every critical AKRITES workflow can name the owner, reviewer, approval gate, escalation path, stop authority and evidence record.
Deploy within an approved infrastructure boundary, including supported on-premise or private-cloud environments.
AKRITES in action
Choose a capability to see how AKRITES connects trusted knowledge, governed automation and human decisions in one working environment.
Start focused, prove control and value, then expand.
Prove value quickly with a focused process, clear owners and measurable success criteria.
Private deployment, approved knowledge and human approval remain part of the operating model.
Expand proven workflows across teams without rebuilding the governance foundation.
A private demonstration can use one representative workflow to show the experience, controls and evidence your team would receive.
Regulatory context
AKRITES helps organizations operationalize applicable requirements by connecting obligations to owners, processes, controls, evidence and review activities.
Applicable legal and regulatory requirements depend on the organization, sector, jurisdiction, processing activity and criticality. AKRITES supports structured compliance work but does not replace legal interpretation, professional judgement or independent certification.
Business value
Faster research and drafting
More consistent GRC deliverables
Reduced evidence-collection effort
Clearer ownership and follow-up
Measure value through cycle time, audit preparation hours, backlog, rework, evidence completeness, SLA performance, external service costs and the capacity released from repetitive coordination.
From demonstration to pilot
Start with a focused process, inspect the controls and evidence, and leave with a practical basis for a pilot decision.
Choose one representative GRC process, its owner, boundaries and success criteria.
Work with sanitized examples or material your organization has explicitly approved for the session.
Review sources, generated deliverables, human approval points, evidence and deployment fit.
Document the pilot scope, technical dependencies, owners and measures that matter to your team.
FAQ
No. AKRITES accelerates research, drafting, comparison, evidence collection and workflow coordination. Accountable professionals remain responsible for review, judgement, approval and risk acceptance.
AKRITES supports customer-approved deployment models such as on-premise, private-cloud or controlled VPC environments. The exact architecture and data boundary are defined for each implementation.
Yes. Approved documents and repositories can be connected to the knowledge layer according to access rights, classification and source-governance rules.
Source references can be included for workflows based on retrieved organizational knowledge. The exact citation and evidence behaviour is configured according to the use case.
Only when the workflow, tool permissions, action limits, approval gates and exception rules have been explicitly defined. High-risk outcomes can remain subject to mandatory human approval.
No software platform can guarantee compliance by itself. AKRITES helps organizations structure requirements, controls, evidence and workflows. Legal interpretation, management accountability and certification remain with qualified professionals and the organization.
AKRITES is designed for controlled integration with approved document repositories, identity systems, GRC platforms, ticketing systems, APIs and internal tools. Only integrations that are actually available should be named publicly.
The modular architecture can support selected private, local or approved hosted models. Model choice depends on security, quality, language, infrastructure and use-case requirements.
Private demonstration
See how AKRITES can support one of your existing audit, risk, privacy, security or compliance processes using your approved knowledge and control requirements.